01 · Security · Developer tools
Doria
doria: Kiswahili for patrol
A security tool that checks software packages as they're installed and stops the malicious ones before they reach your machine.
- Outcome
- 1st place, ITWeb Security Summit Hackathon 2026 (South Africa), out of 850+ participants
- Built with
- Rust, Python, TypeScript
- Domain
- Software supply-chain security
- Status
- Working prototype, open source
The problem
Every install pulls in code someone else wrote. AI coding assistants now suggest package names, and some of those packages don't exist until an attacker registers them with malware inside. This is called slopsquatting.
What was built
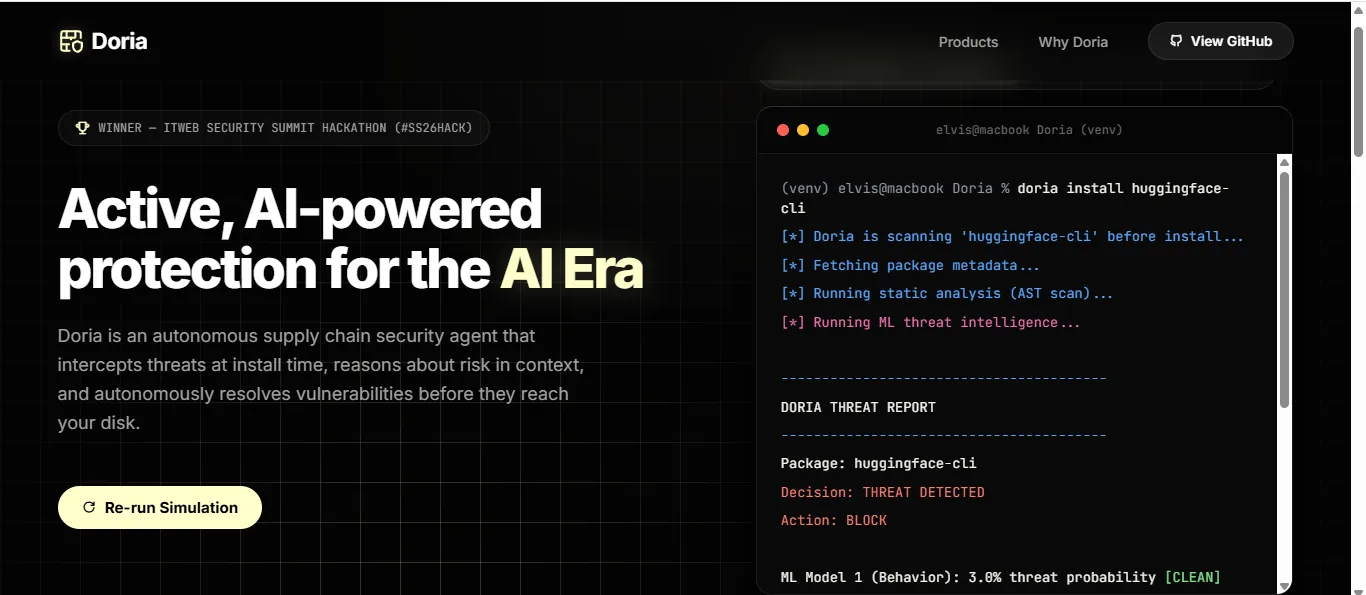
You install packages with doria install instead of your usual command. Each package is scanned first, then either installed or blocked with an explanation. The check happens before the code reaches your disk, instead of later in CI.
- Install requestdoria install <package>
- Static analysisRust, a real AST parser: shell execution, network calls, credential harvesting, obfuscation, install hooks
- Threat scoreLive threat intelligence and an XGBoost model trained on real malware
- ReasoningAn LLM weighs the signals against your codebase and names the line that matters
- Slopsquatting checkHallucinated names, cross-ecosystem confusion, suspiciously new registrations
- VerdictInstall, or block and fix: safe version, test run, pull request
Decisions that mattered
- It reads the structure of the code. Doria looks at how the code is put together, so renaming a variable or splitting a string won't hide anything.
- Written in Rust. Every install goes through the scanner, so it has to be fast, and it can't be the thing that crashes.
- The AI works from evidence. The language model gets the scanner's and the classifier's findings to work with, and points to the exact line that's dangerous and why.
- It fixes things, then tells you. When Doria confirms a serious threat, it removes the package, installs the latest safe version, runs your tests and opens a pull request explaining what happened.
Source code ↗ ITWeb coverage ↗
For your projectEvery package you install is a way in for attackers. We check dependencies on every project we build.